A med spa website can look professional, load quickly, and rank well in Google while still having privacy and security issues that need attention. The biggest concerns usually appear when a website collects, transmits, stores, or provides access to protected health information (PHI) through forms, booking tools, patient portals, chat, uploads, or third-party integrations.
A HIPAA-compliant med spa website therefore involves more than installing an SSL certificate. A proper review should examine how patient information moves through the website, which vendors receive it, how access is controlled, and whether appropriate safeguards and agreements are in place.
This 10-point med spa website audit checklist covers the main areas to review, from secure forms and online booking to analytics, tracking pixels, hosting, access controls, and risk analysis.
What Makes a Med Spa Website HIPAA Compliant?
HIPAA compliance depends on how a covered entity or business associate handles PHI and electronic protected health information (ePHI). The HIPAA Security Rule requires appropriate administrative, physical, and technical safeguards to protect the confidentiality, integrity, and availability of ePHI.
For a med spa, the website may become part of that environment when it collects information such as a patient’s name, contact details, medical history, treatment information, appointment information, or other individually identifiable health information.
A general service page that simply explains a treatment is different from a consultation form that asks about a patient’s medical history. The important question is not only what the page looks like, but what information the website collects and where that information goes.
10-Point Med Spa Website HIPAA Audit Checklist
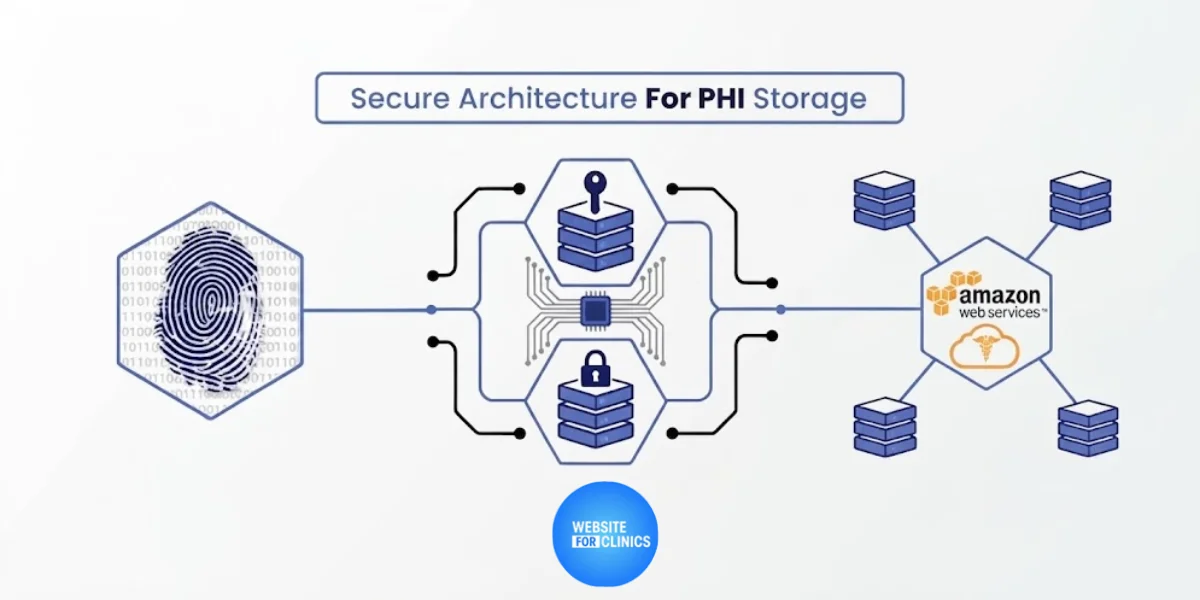
1. Check SSL/TLS Encryption and Data Transmission
Start with the basics. Confirm that the website uses HTTPS and has a valid SSL/TLS certificate.
Encryption helps protect information while it travels between the visitor’s browser and the website. However, HTTPS alone does not make a website HIPAA compliant. HHS notes that encryption is only one part of protecting ePHI and does not replace other administrative, physical, and technical safeguards.
During the audit, check:
- HTTPS across the entire website
- Valid and properly configured SSL/TLS
- Secure redirects from HTTP to HTTPS
- Secure transmission of form submissions
- No sensitive information being passed through unsecured URLs
2. Audit Patient Intake and Appointment Forms
Forms deserve close attention because they are often where patient information first enters the website.
Review every patient intake form, consultation form, contact form, and appointment form. Determine what information each form collects and where the submission is sent.
For example, a basic request for a name and phone number may have different privacy considerations from a form asking about medical conditions, medications, previous procedures, or treatment history.
Check whether form submissions:
- Are transmitted securely
- Are stored securely
- Are accessible only to authorized staff
- Avoid unnecessary collection of sensitive information
- Connect to an appropriate healthcare or business system
- Are handled by vendors that have been properly evaluated
Do not assume a form is secure simply because the website uses HTTPS.
3. Review Online Booking and Patient Communication
Online booking can improve the patient experience, but the booking system should also be included in your website compliance review.
Look at every tool used for:
- Appointment scheduling
- Consultation requests
- Live chat
- Patient messaging
- Email notifications
- SMS communication
- Automated appointment reminders
Ask what information each tool collects and whether that information can include PHI.
If a patient enters a reason for seeking treatment or other health information during the booking process, that data flow needs to be reviewed carefully.
The same applies to patient communication tools. A convenient chat widget is not automatically appropriate for handling sensitive health information.
4. Verify Business Associate Agreements With Third-Party Vendors
Your website may rely on several third-party services. These can include hosting companies, form platforms, booking software, CRMs, storage systems, communication tools, and other integrations.
If a vendor is acting as a business associate and creates, receives, maintains, or transmits PHI on behalf of a covered entity, HIPAA requires an appropriate Business Associate Agreement (BAA). HHS explains that BAAs establish permitted uses and disclosures of PHI and require business associates to comply with applicable HIPAA requirements.
Create a list of every service connected to the website and determine:
- What data it receives
- Whether PHI can reach the service
- How the data is protected
- Whether a BAA is applicable
- Who has access to the information
- Where the information is stored
A website should not be treated as isolated from the rest of the clinic’s technology environment.
5. Audit Google Analytics, Tracking Pixels, and Advertising Tools
Analytics and advertising tools deserve special attention on healthcare websites.
Review Google Analytics, Meta Pixel, remarketing scripts, cookies, session recording tools, and other tracking pixels installed on the website.
The issue is not simply whether analytics is installed. The important question is whether tracking technology collects or transmits information that is subject to HIPAA protections.
HHS specifically warns that tracking technologies can collect information such as IP addresses, appointment information, contact details, and other identifiers. Where the information constitutes PHI, HIPAA requirements can apply to disclosures to tracking technology vendors.
For a med spa website audit, review:
- Tracking scripts on forms
- Booking pages
- Patient portal pages
- Consultation pages
- URLs and query parameters
- Event tracking
- Remarketing tags
- Session replay tools
- Data sent to third-party vendors
Do not assume that adding a privacy policy or cookie banner automatically resolves a HIPAA issue. HHS states that a privacy policy alone does not authorize an impermissible disclosure of PHI to a tracking technology vendor.
6. Check Hosting, Storage, and Website Security
Your website’s hosting environment is another important part of the audit.
Review how website data is stored, backed up, accessed, and protected. If a hosting provider handles ePHI on behalf of a covered entity, the relationship and applicable BAA requirements should be evaluated.
A proper website security review should consider:
- Hosting environment
- Server access
- Backups
- Software updates
- Plugin security
- Malware protection
- Administrative access
- Data storage
- Security monitoring
HHS emphasizes that protecting ePHI requires more than encryption alone. Safeguards also need to address risks to confidentiality, integrity, and availability.
7. Review Access Controls and Staff Logins
A secure website should not give every employee the same level of access.
Review administrator accounts and confirm that staff use individual credentials rather than shared logins. Access should be limited according to each person’s responsibilities.
Check for:
- Unique user accounts
- Strong passwords
- Multi-factor authentication where appropriate
- Role-based permissions
- Restricted administrator access
- Removal of former employee accounts
- Regular access reviews
These controls are particularly important when website administrators can access forms, patient information, integrations, or systems connected to the website.
8. Audit Patient Photos, File Uploads, and Portals
Med spa websites may handle more than text-based forms.
Before-and-after photos, consultation images, medical documents, file uploads, and patient portals can all introduce additional privacy and security considerations.
During an audit, identify every location where a patient can upload or access information.
Check:
- Photo upload forms
- Consultation documents
- Patient portals
- Medical file uploads
- Downloadable patient information
- Storage locations
- User permissions
- Third-party file services
The goal is to understand the complete patient information flow, not just the public-facing website.
9. Find Old Forms, Staging Sites, and Forgotten Website Data
One commonly overlooked part of a HIPAA website audit is finding old website assets.
A clinic may have an old campaign landing page, staging website, test form, unused plugin, or forgotten subdomain that is still accessible.
Check for:
- Staging websites
- Old landing pages
- Campaign forms
- Test submissions
- Unused subdomains
- Old plugins
- Previous booking integrations
- Forgotten tracking scripts
These assets should be reviewed because an outdated website component can create security or privacy risks even when the main website has been redesigned.
10. Document Website Data Flows and Risk Analysis
The final step is to document what you discovered.
HHS describes risk analysis as a foundational requirement for identifying risks and vulnerabilities affecting ePHI. It involves assessing the systems and applications used to access and store data and considering the potential impact of security weaknesses.
For your website, document:
- Where patient information enters
- What information is collected
- Where the information is transmitted
- Where it is stored
- Which vendors receive it
- Who can access it
- What safeguards are in place
- What risks need to be addressed
HIPAA compliance is not a one-time website setting. HHS explains that organizations should perform risk analysis, implement reasonable and appropriate security measures, maintain documentation, and evaluate their information security environment over time.
How to Make a Med Spa Website HIPAA Compliant
If your audit identifies problems, start with the data rather than redesigning the entire website.
First, identify every place where PHI can enter the website. Next, map where that information travels and which vendors receive it. Then review applicable BAAs, security controls, access permissions, forms, booking systems, analytics, and storage.
You may also need to reduce unnecessary data collection. If a form does not need a specific piece of sensitive information to accomplish its purpose, collecting it may create an unnecessary risk.
The process should be:
Identify → Map → Review → Secure → Document → Monitor
A formal HIPAA compliance program should be handled with the appropriate legal, privacy, security, and healthcare professionals for the clinic’s circumstances.
Common Med Spa Website Compliance Mistakes to Avoid
Some of the most common mistakes are simple assumptions:
- Assuming HTTPS automatically makes a website HIPAA compliant
- Sending sensitive patient information through ordinary email
- Installing third-party tools without reviewing their data practices
- Ignoring Google Analytics and tracking pixels
- Collecting more patient information than necessary
- Giving too many employees administrative access
- Using shared website credentials
- Forgetting old staging websites and campaign pages
- Treating a privacy policy as proof of HIPAA compliance
A strong med spa website compliance strategy looks at the complete information flow instead of relying on one security feature.
HIPAA-Compliant Website Design for Med Spas
A med spa website should protect patient information without creating a poor user experience.
Good HIPAA-compliant website design should bring together secure functionality, clear treatment information, mobile usability, accessible booking, website security, and an SEO-friendly structure.
The public-facing website still needs to help prospective patients understand treatments, meet the providers, find the clinic, and take the next step. At the same time, any functionality that collects or handles PHI should be designed and integrated appropriately.
This is one reason custom planning can be useful for clinics with more complex requirements. Instead of forcing every function into a generic template, the website structure can be built around the clinic’s actual patient journey, integrations, and technical requirements. For clinics comparing approaches, Templates vs Custom Web Design for Medspas can help explain the differences between a template-based and custom website strategy.
A strong medical spa website design should therefore consider both patient experience and the technical environment behind the website.
When Should You Get a Med Spa Website Audit?
A med spa website audit can be useful before launching a new website or whenever your technology changes.
Consider an audit when:
- Launching a new website
- Adding online booking
- Adding patient intake forms
- Connecting a CRM
- Installing new analytics
- Adding advertising pixels
- Changing hosting providers
- Adding chat or messaging
- Integrating a patient portal
- Redesigning an older website
An audit can also help identify outdated plugins, unnecessary data collection, forgotten integrations, or unclear data flows.
If your clinic already has a website but you are unsure how forms, booking, analytics, hosting, and third-party tools handle patient information, med spa website audit services can provide a structured way to identify areas that need further review.
Build a Secure, Search-Friendly Med Spa Website
HIPAA considerations should not mean sacrificing search visibility or patient experience.
A modern med spa website needs to balance patient data security, website security, SEO, mobile performance, treatment content, online booking, and clear conversion paths.
Your public pages should make it easy for prospective patients to understand services and find the information they need. At the same time, sensitive workflows should be reviewed separately to determine how information is collected, transmitted, stored, and accessed.
For clinics planning a redesign, Medical Spa Website Practices can also help guide decisions around structure, usability, content, and the overall patient experience.
The cost of building or redesigning a website depends on its design, functionality, integrations, content, and technical requirements. Clinics evaluating their investment can also consider aesthetic clinic website design cost when planning a healthcare-focused website project.